Continuous compliance, by construction
Audit, remediate, and enforce compliance policies across all your cloud infrastructure automatically.
Govern your cloud automatically
Audit what's already running, let agents write the fixes, and block violations before the next deploy.
Audit
Continuous scans check the infrastructure you already run against CIS, NIST, and PCI DSS.Remediate
Agents write fixes automatically, and hours of manual remediation become a quick review and merge.Prevent
Policy guardrails block non-compliant deployments automatically, before they reach production.
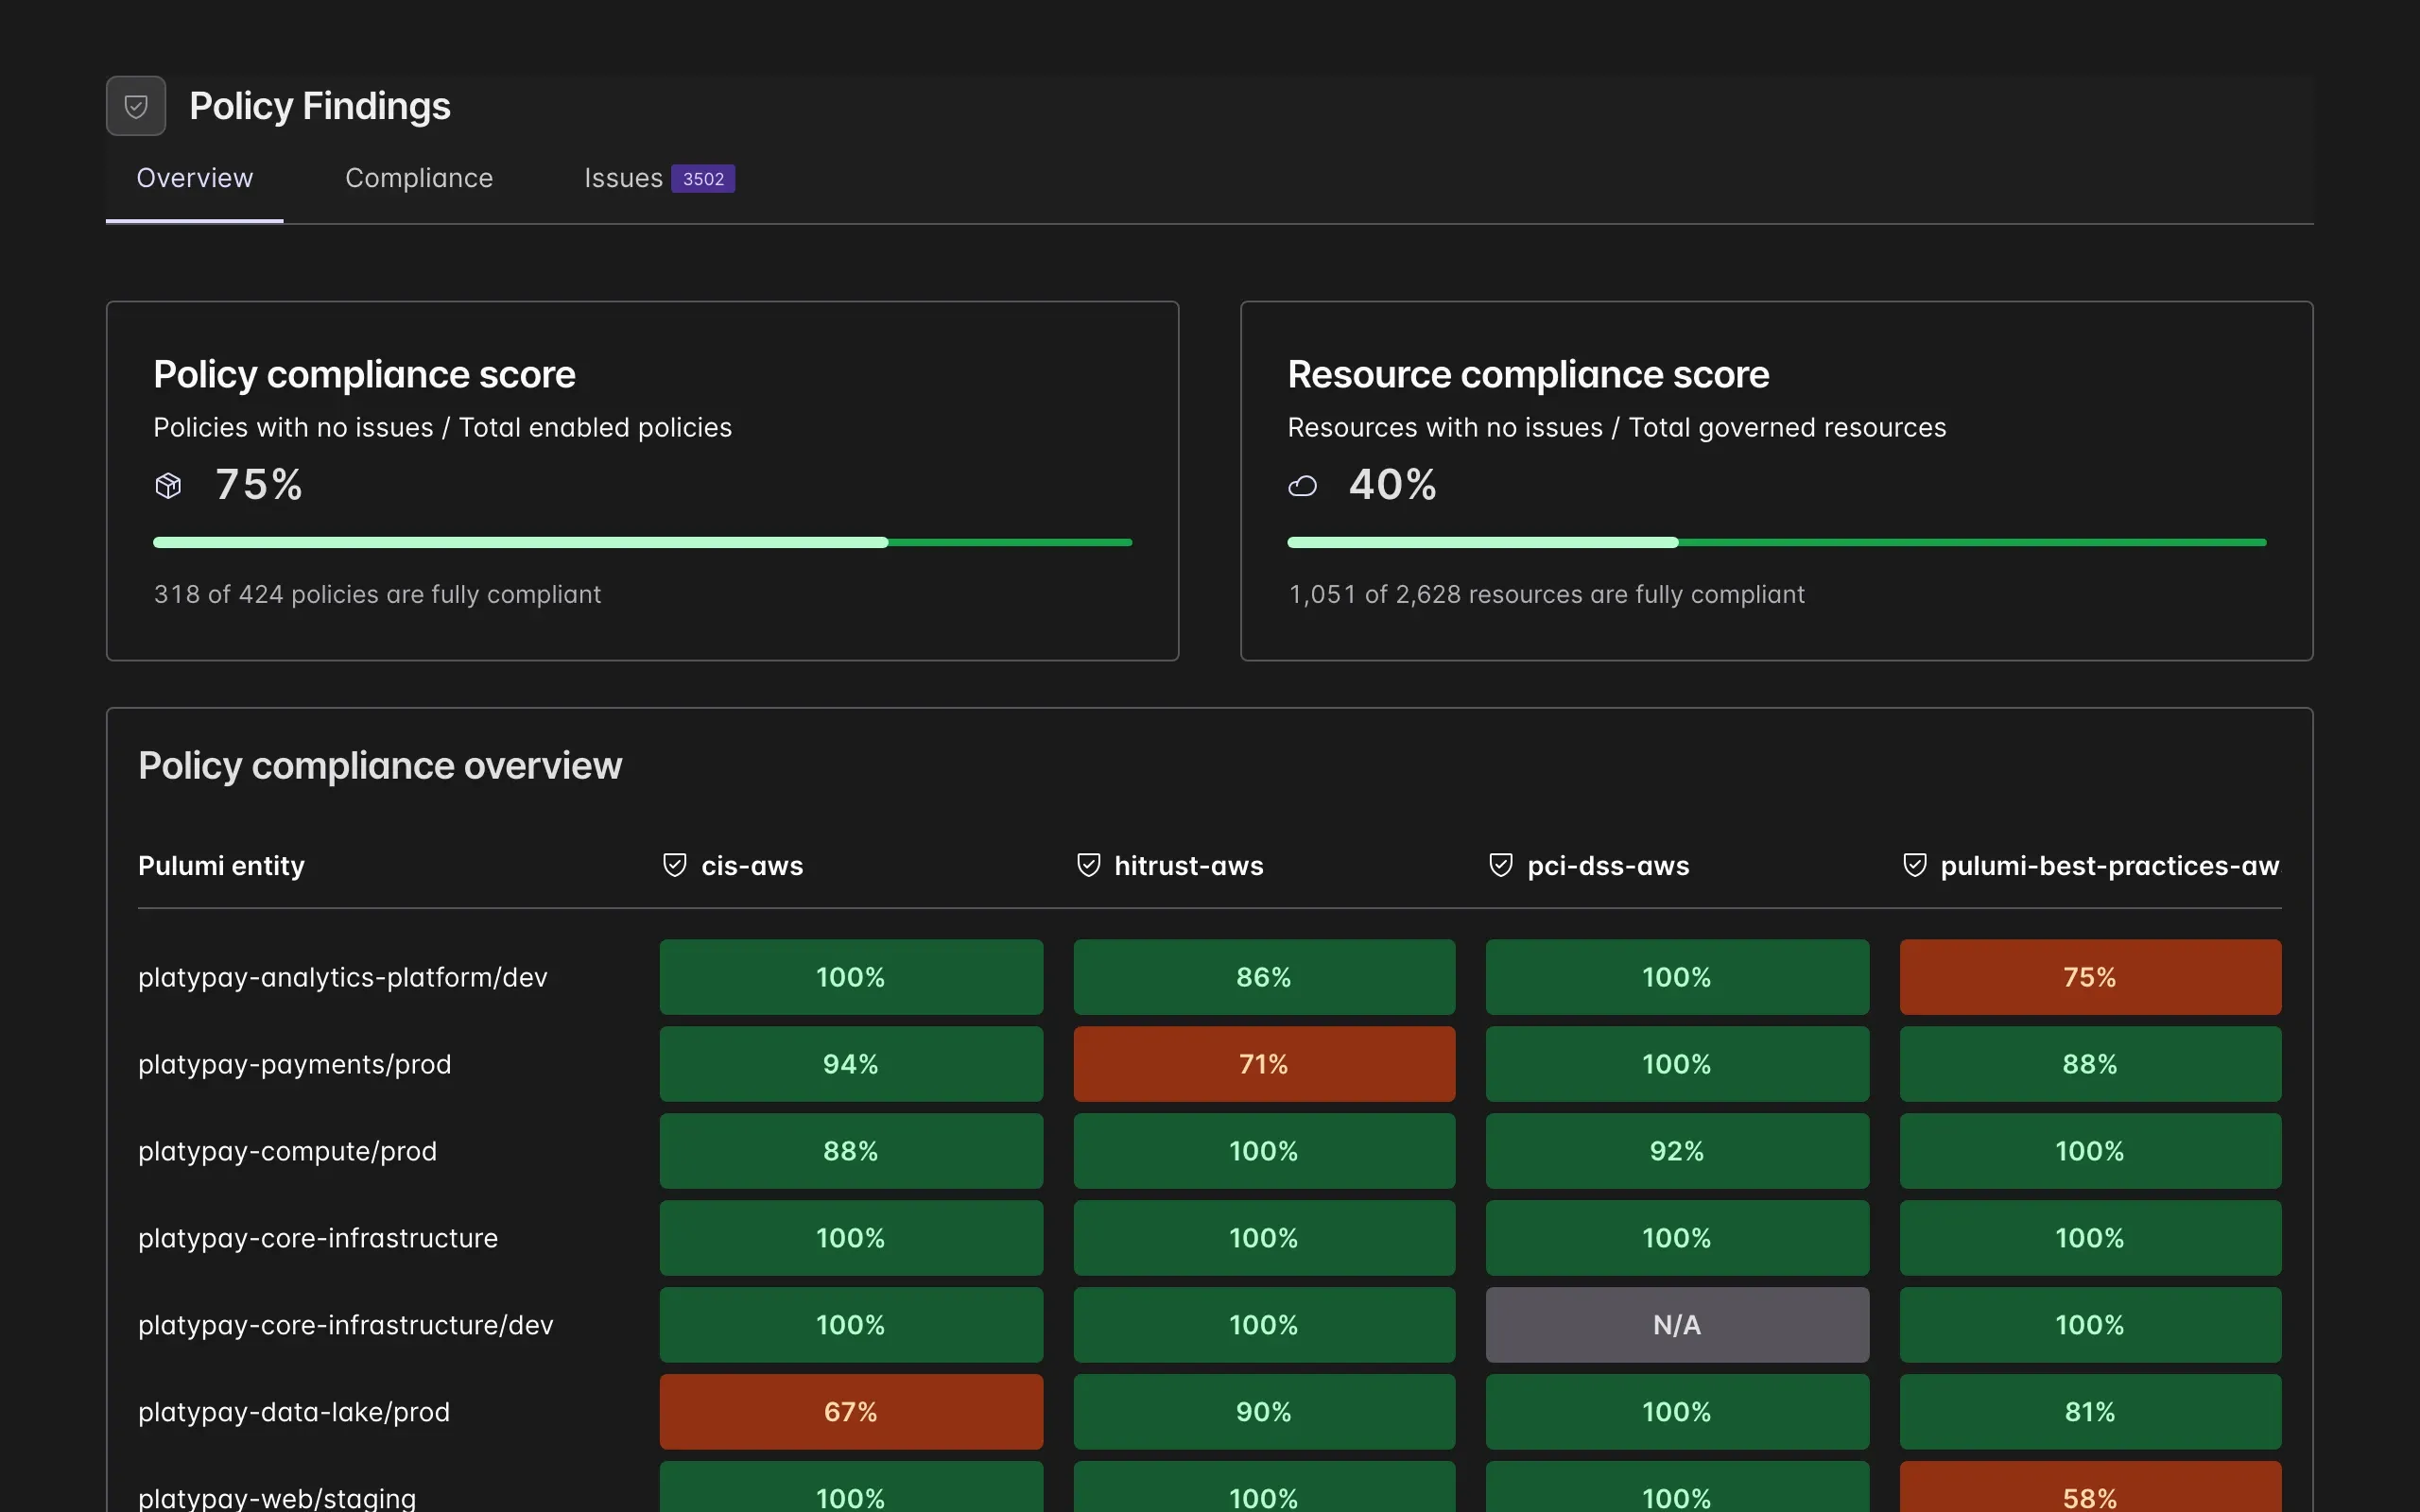
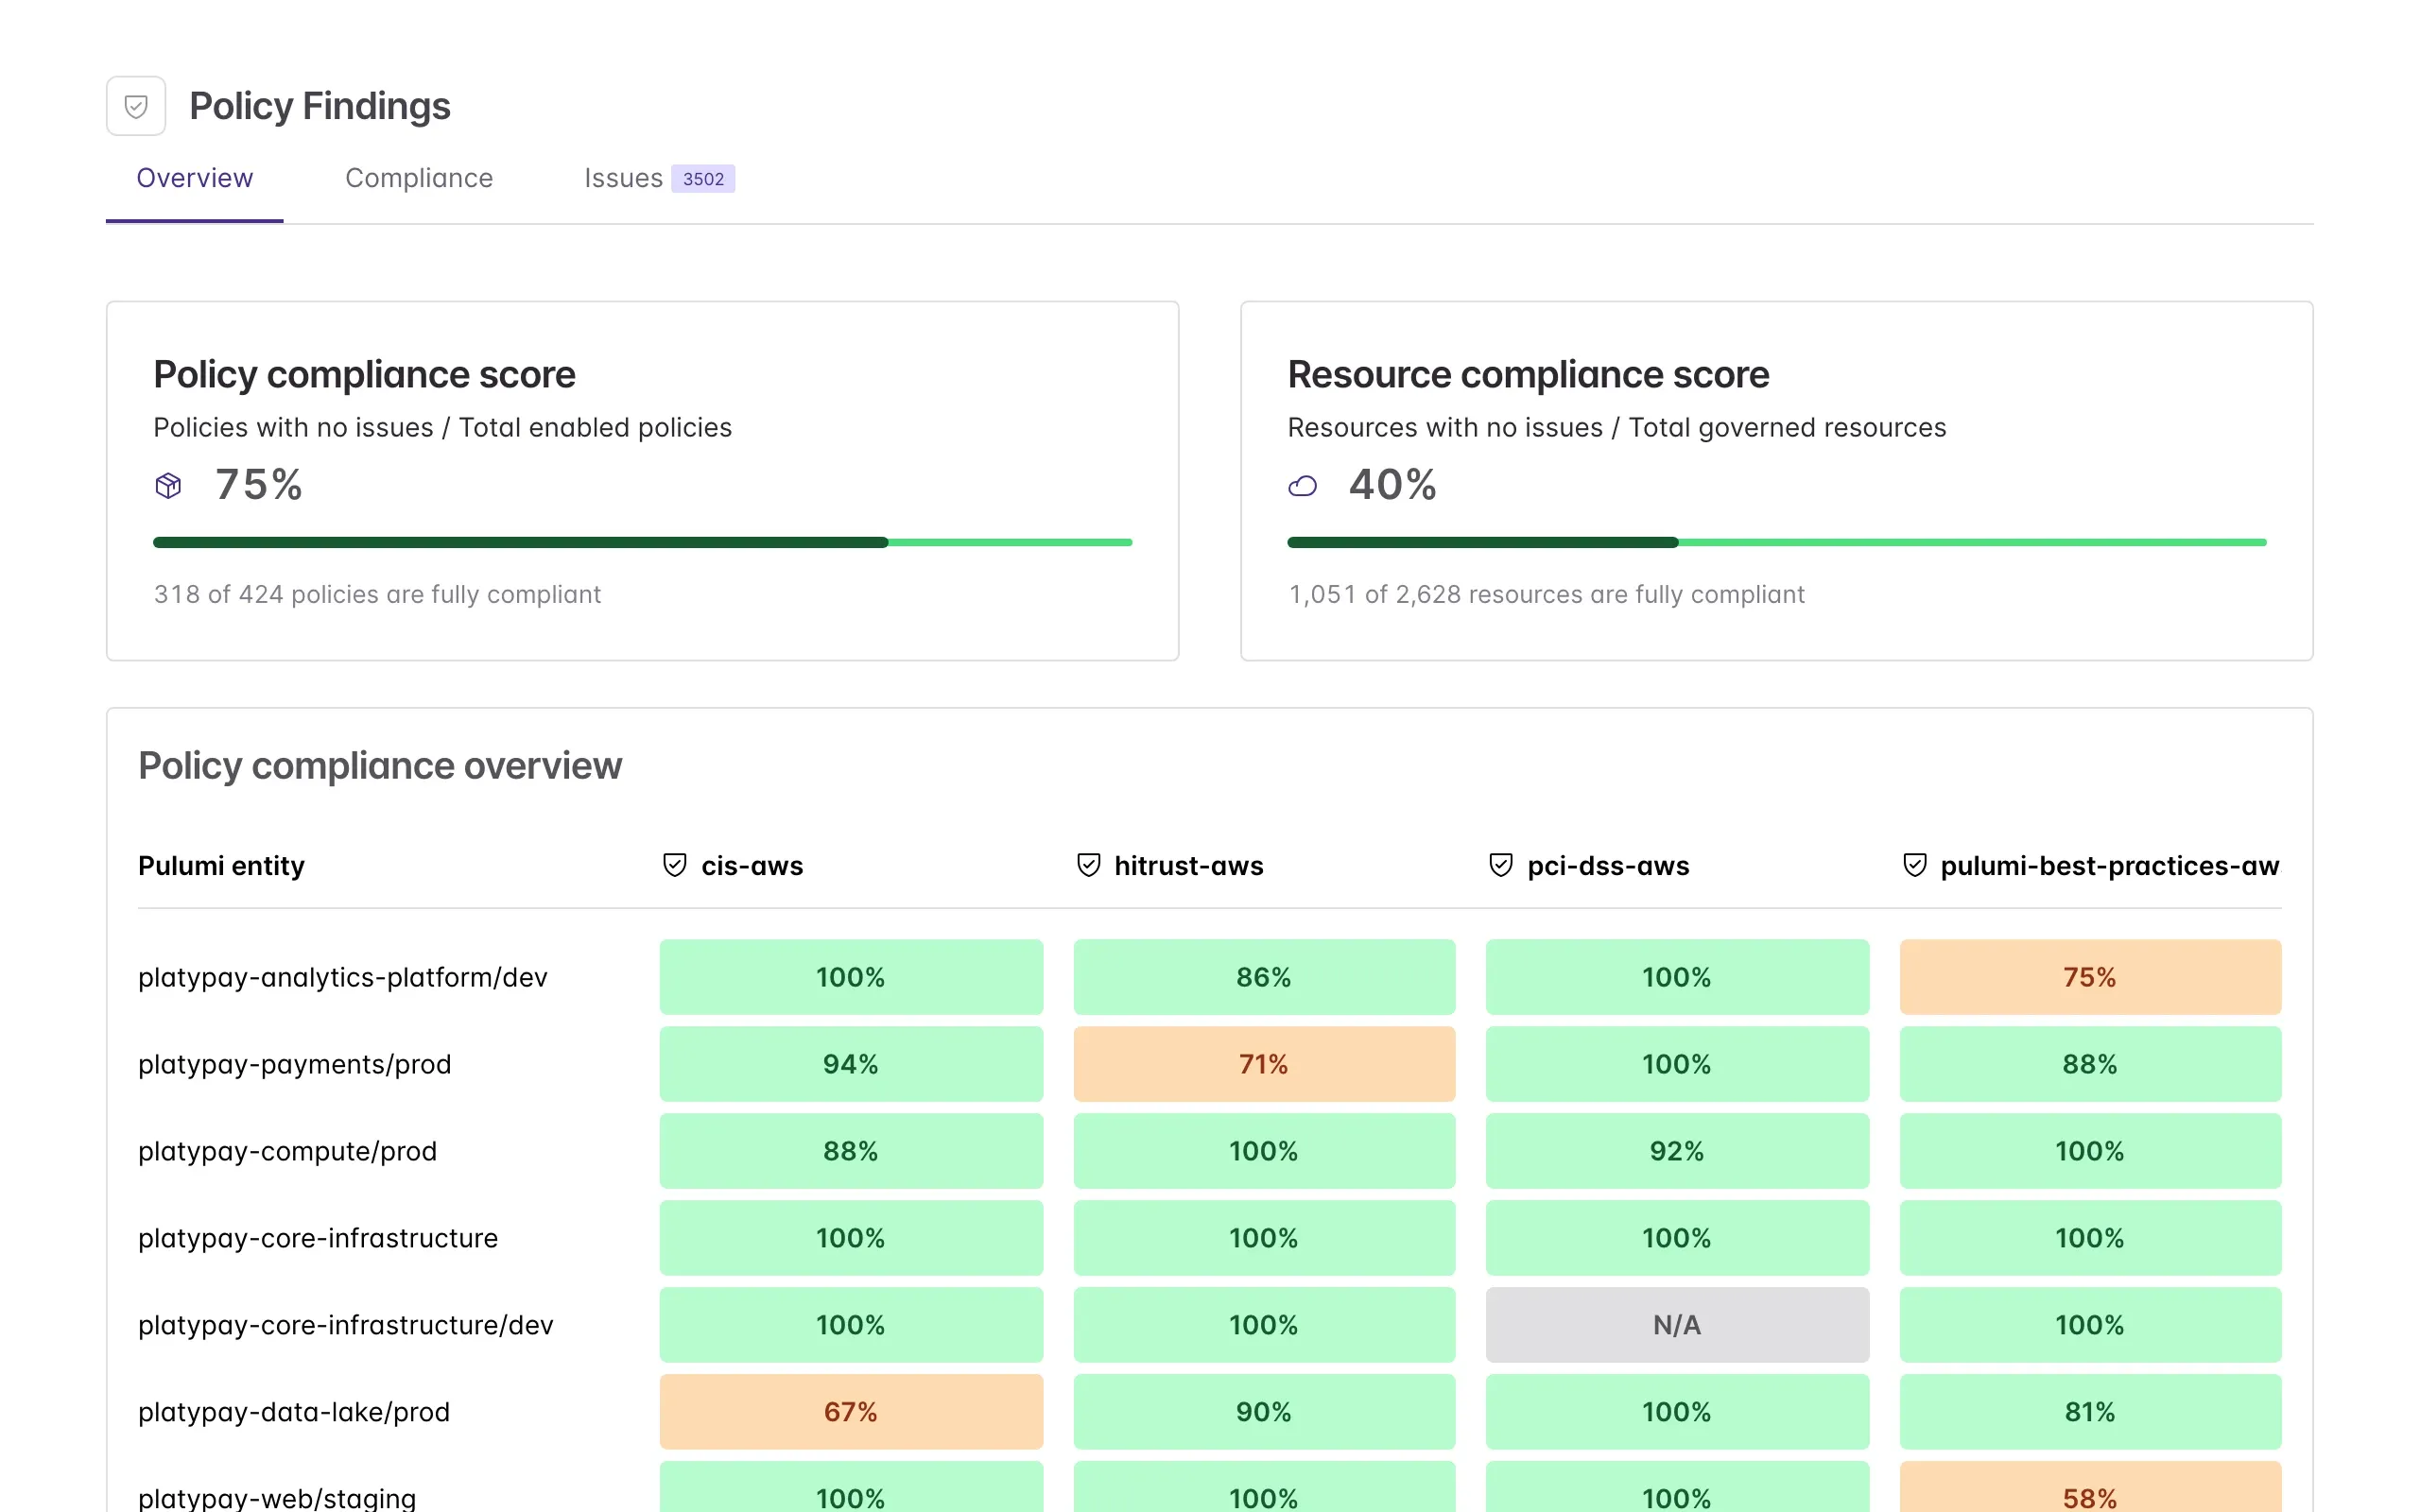
Audit existing infrastructure against compliance standards
Continuous scans check everything you run against CIS Controls, NIST SP 800-53, HITRUST CSF, and PCI DSS — including infrastructure built with Terraform, CloudFormation, or by hand. Run them on demand or after every deployment, and hand auditors a report they can use.

“We gave our auditors access to our policy packs because it’s far easier to understand and prove controls in code than in docs and diagrams. With Pulumi’s Policy as Code approach, that manual review process has gone away. We’ve reduced our Authority to Operate (ATO) timeline from a year and a half to expecting approval in three months.”
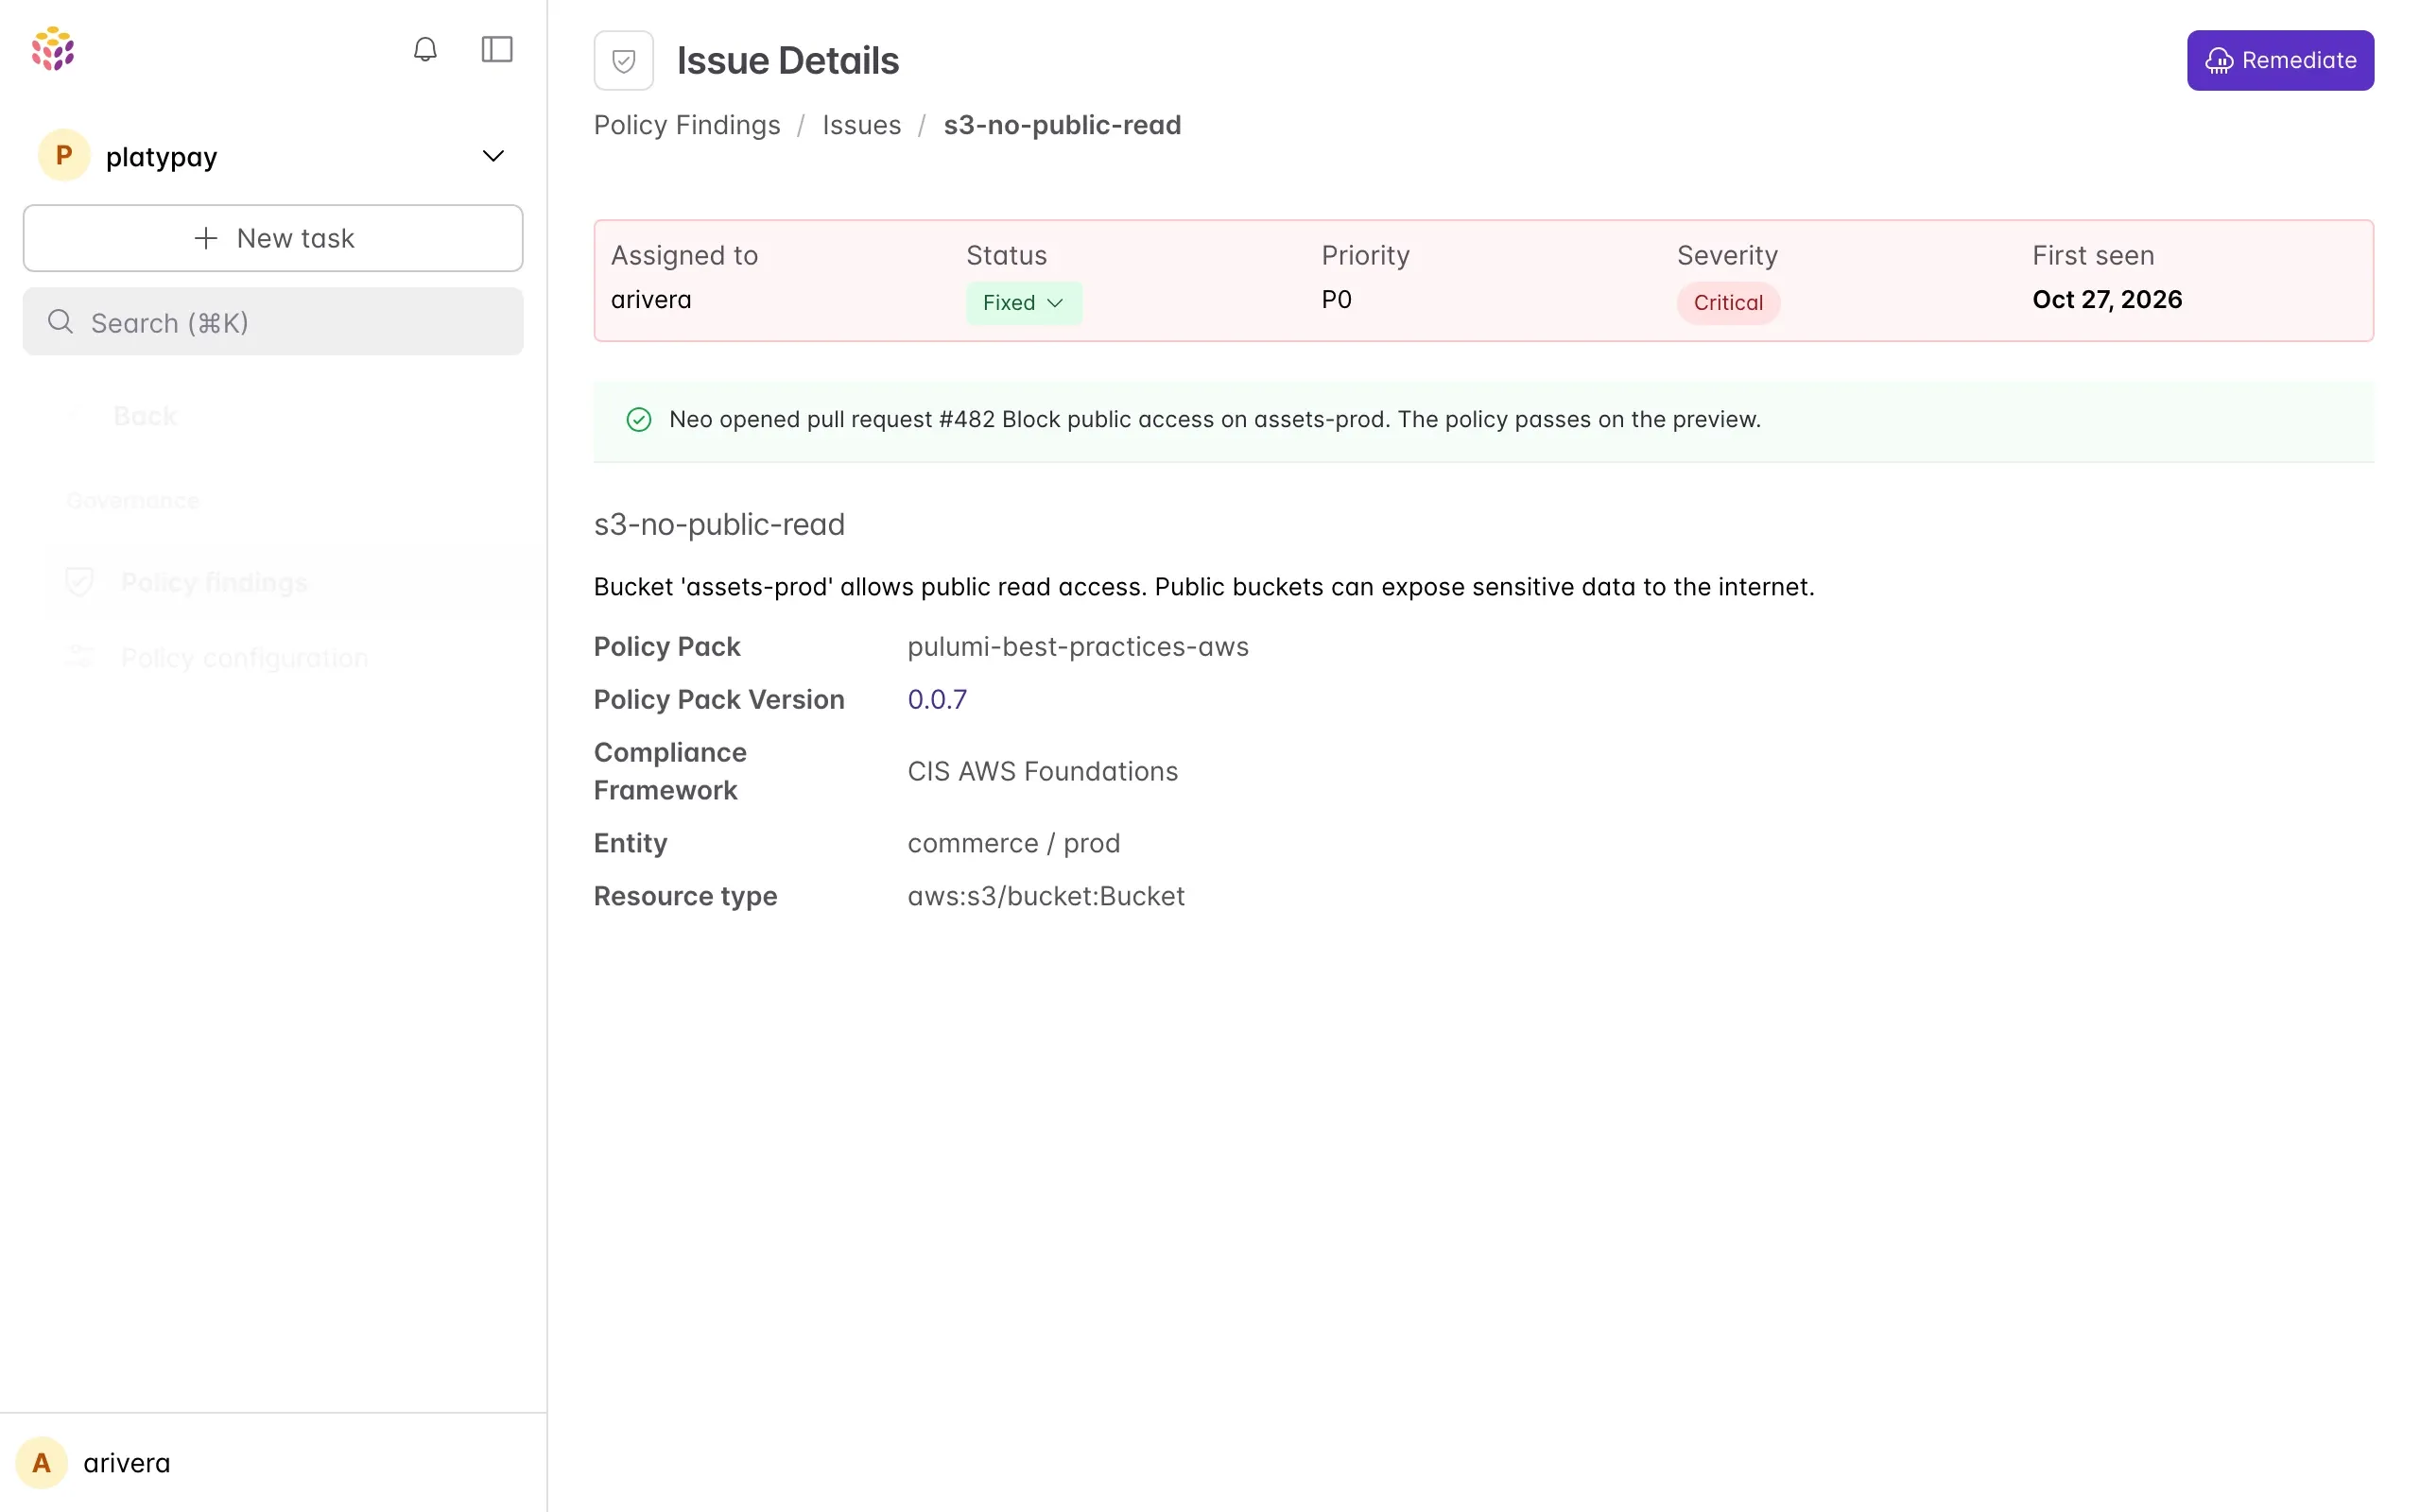
Automatically generate fixes for policy violations
Agents find policy violations, even in unmanaged resources, and open a pull request with the fix for you to review.
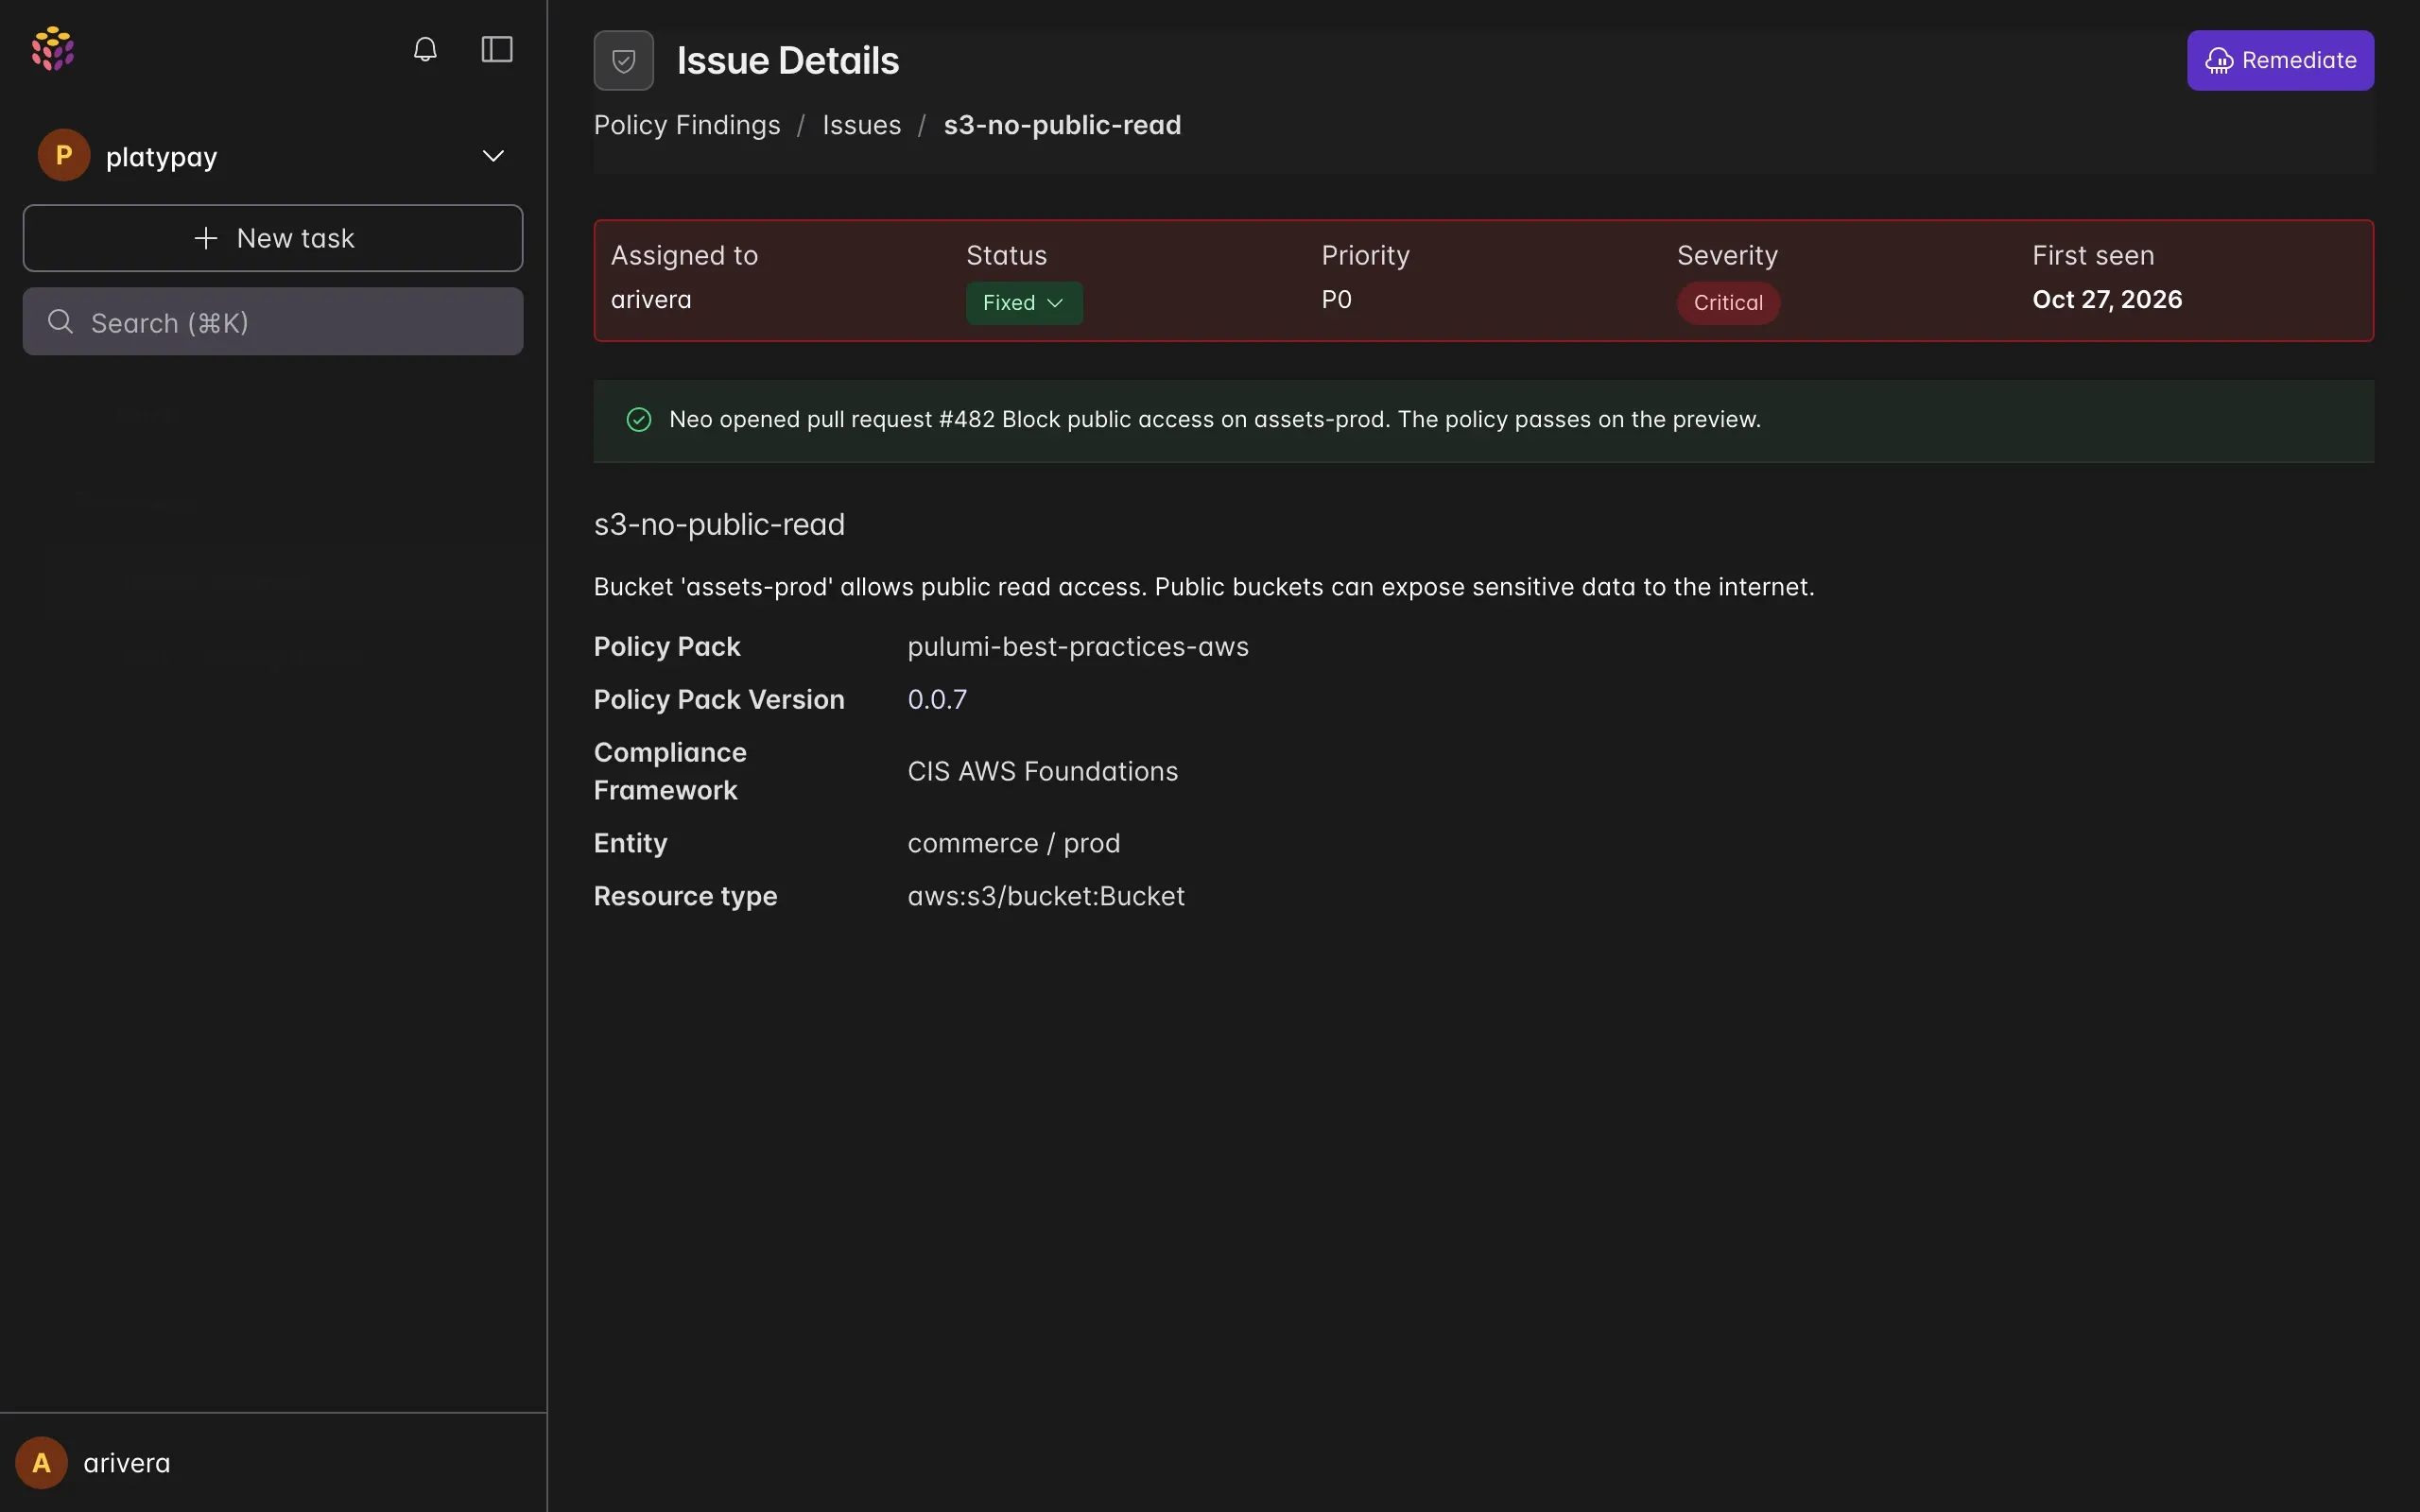
Stop compliance violations before they deploy
Every deployment from both humans and agents runs through the same policies, and non-compliant changes never reach production.
Policies in TypeScript or Python
Write custom rules in languages your team already knows, or deploy pre-built compliance packs.Feedback during deployment
pulumi previewandpulumi upshow which policy failed and why. Start a policy as advisory and make it mandatory later.
Search and understand your entire cloud estate
Query any resource across AWS, Azure, Google Cloud, Oracle Cloud, and Kubernetes with natural language or advanced filters. Pulumi discovers every resource, including unmanaged ones.
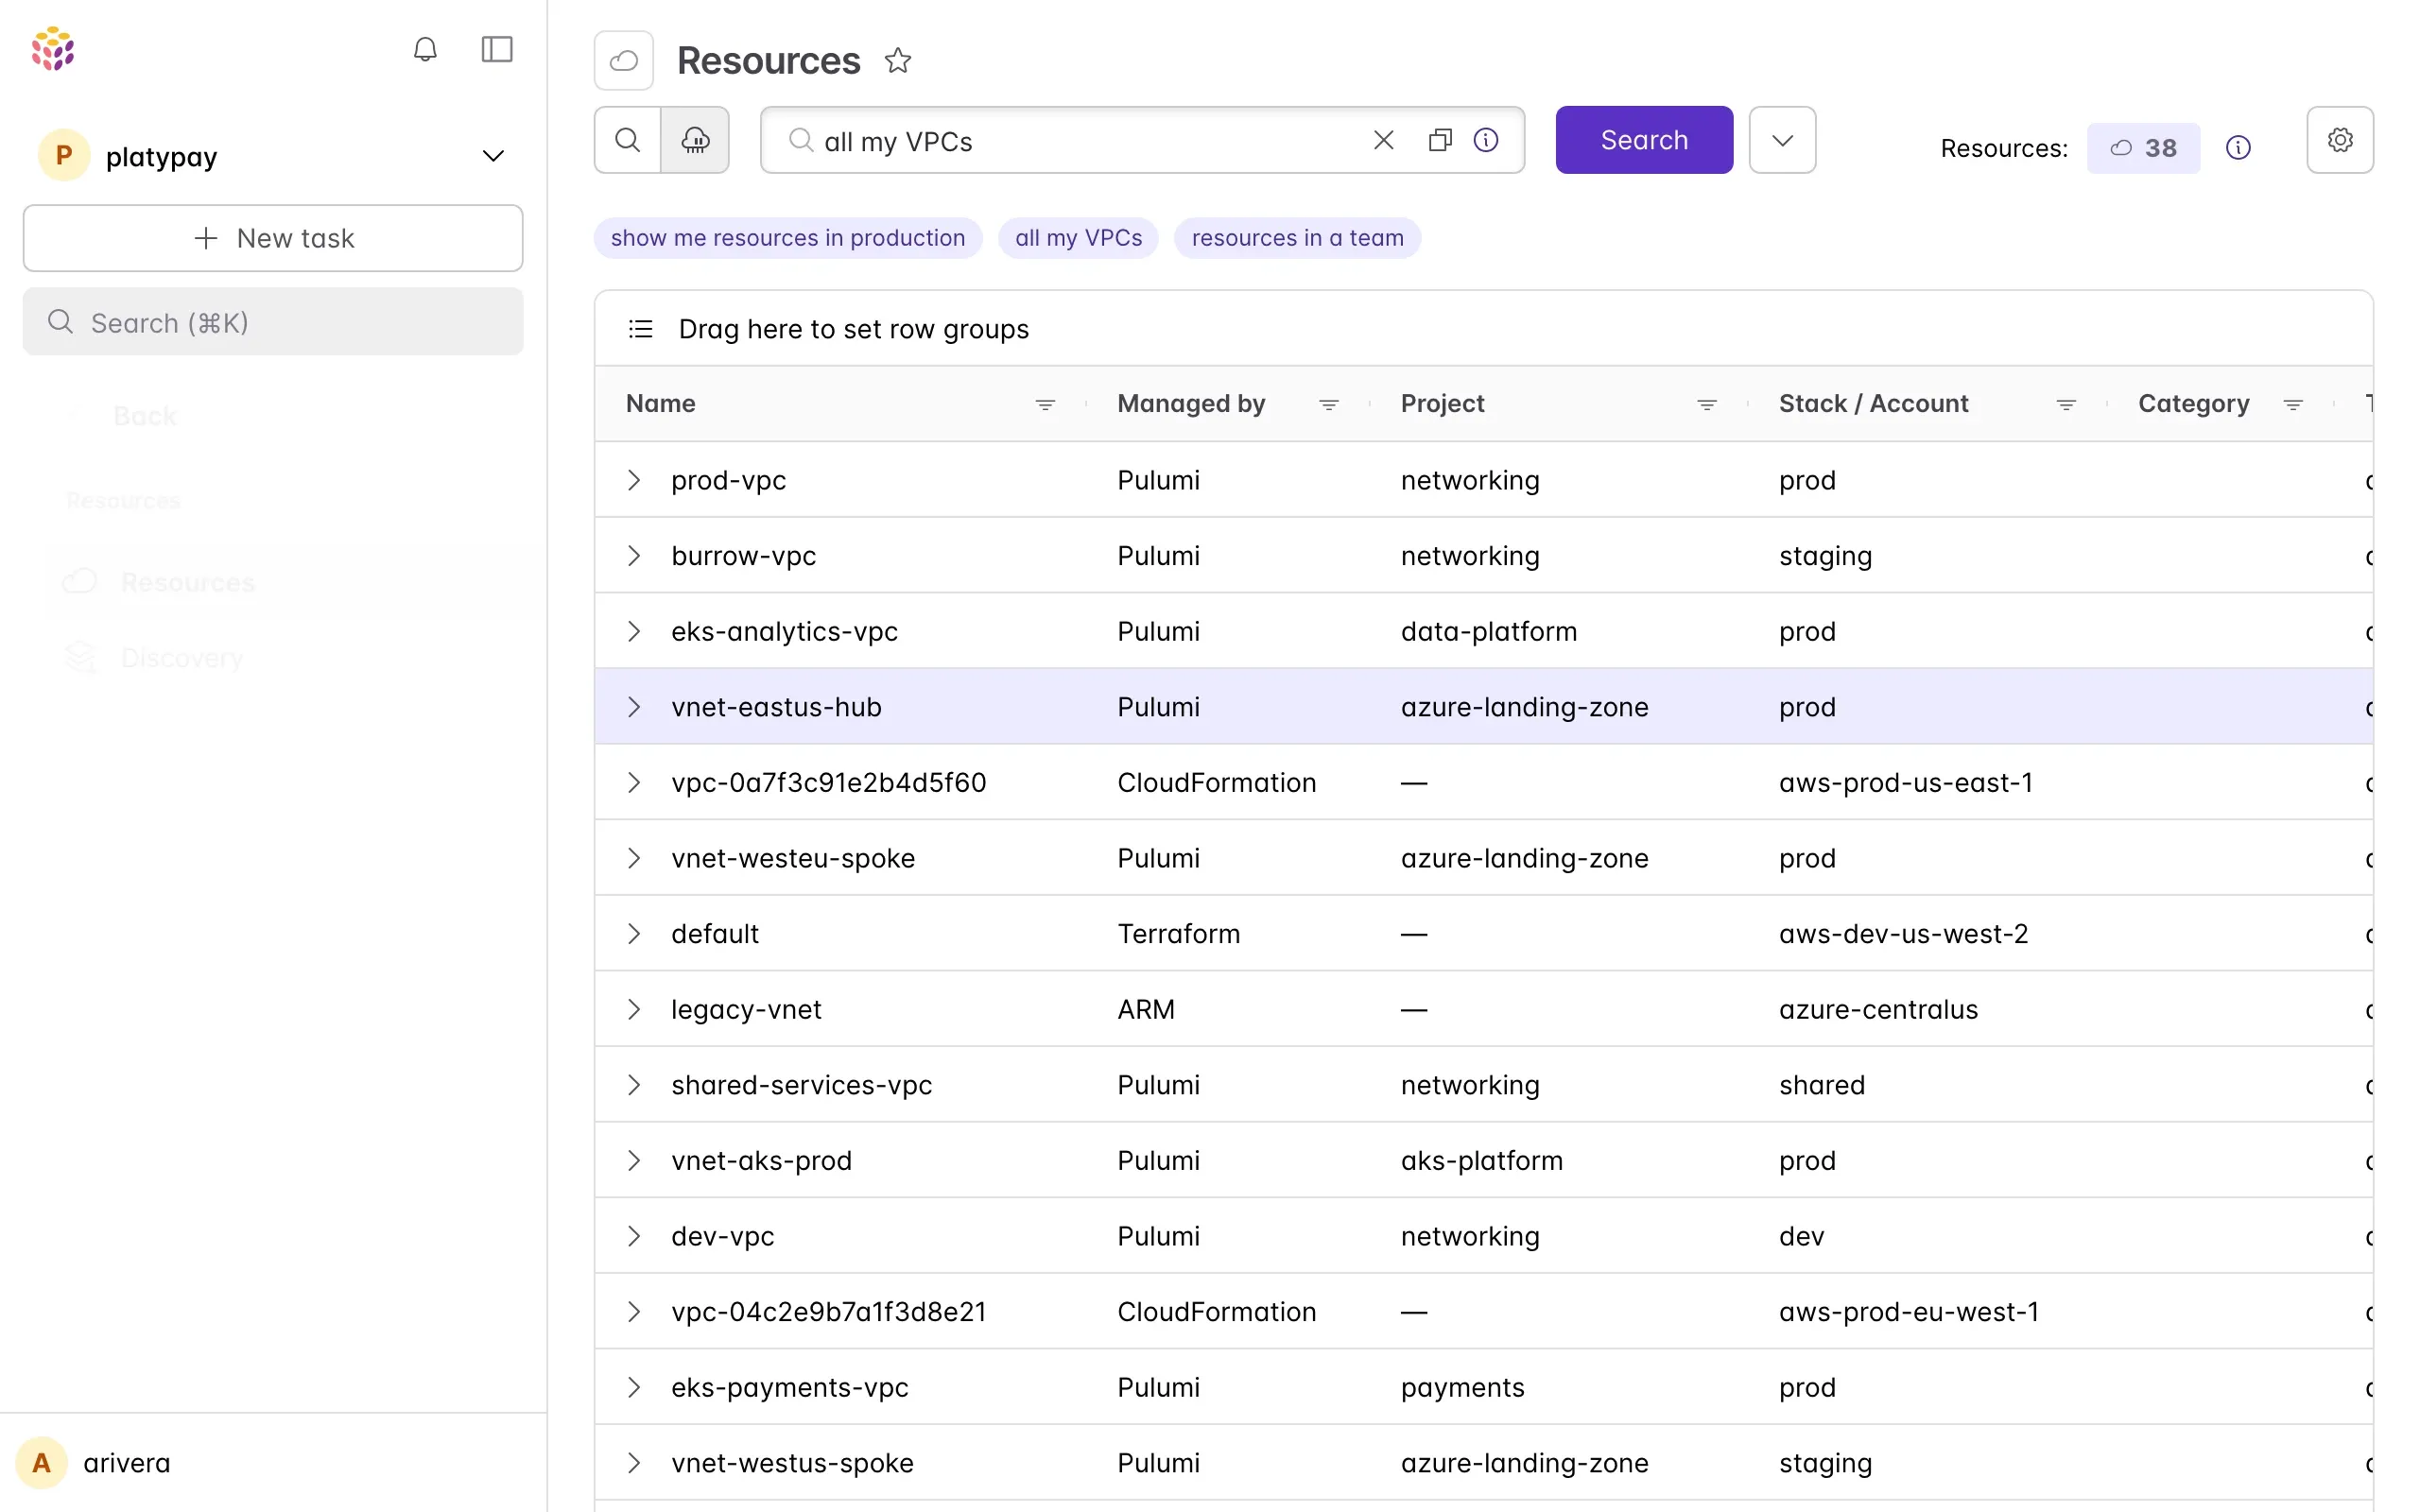
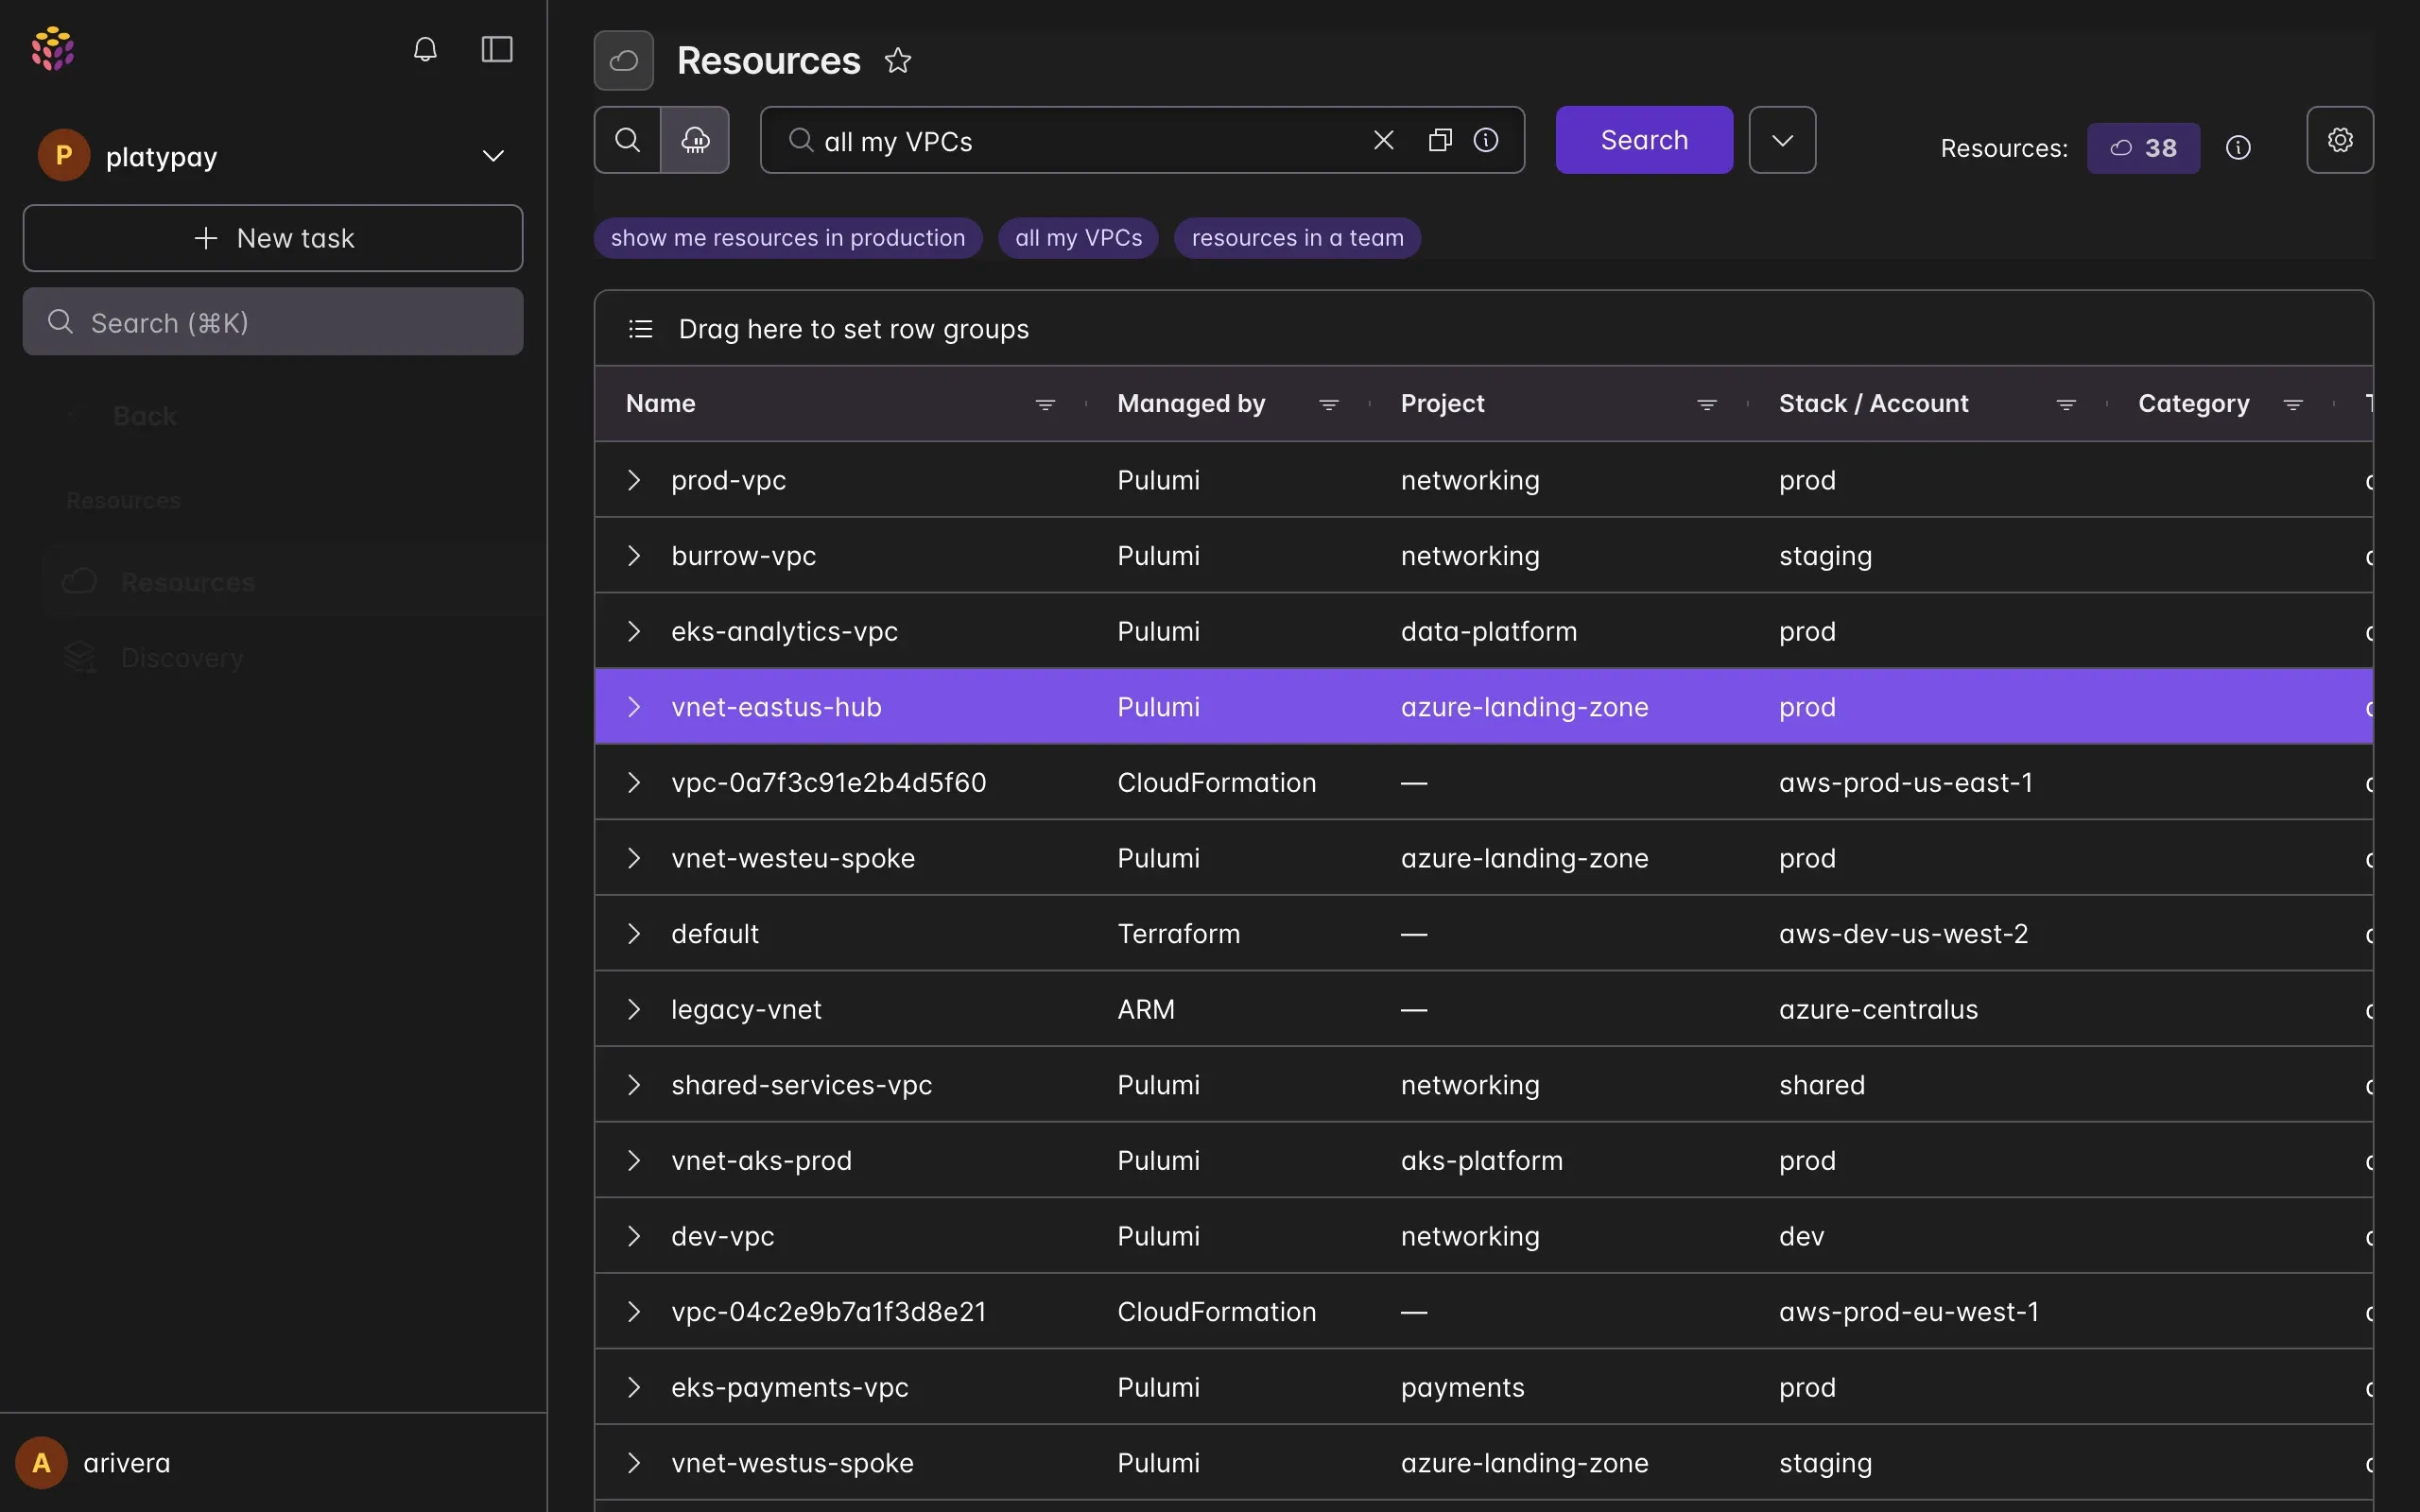
Multi-cloud resource discovery
Scans pick up new resources across every cloud account you connect.Resource relationship mapping
Trace what depends on what before you change or delete a resource.Configuration change history
See every configuration change on a resource, with the values before and after.
Pre-built compliance frameworks
Deploy policy packs that map to industry standards and audit requirements.
Start with complete visibility
Find every resource in your cloud accounts first, then add policies and let agents fix what fails.
Enforce compliance with policy as code
Deploy pre-built compliance packs for CIS, NIST, HITRUST, and PCI DSS, or write custom policies in TypeScript and Python.